Certification

Certified information security, and the documents to prove it

StaffCloud Services Private Limited holds ISO/IEC 27001:2022 for information security and ISO 9001:2015 for quality management. Both certificates are on this page in full, with their numbers, scope, issuing body and audit dates — and both are downloadable, because a security reviewer wants the document rather than a description of it.

  • ISO/IEC 27001:2022
  • ISO 9001:2015
  • Valid to 11 March 2029

The certificates

Click either to see it full size, or download the original PDF. Every field below is transcribed from the document on the right of it.

ISO/IEC 27001:2022

Information Security Management System

Certifies that StaffCloud operates a managed information security system — risks identified, controls chosen against them, owners named, and evidence an auditor has seen. It does not certify that nothing can go wrong; no certificate does that.
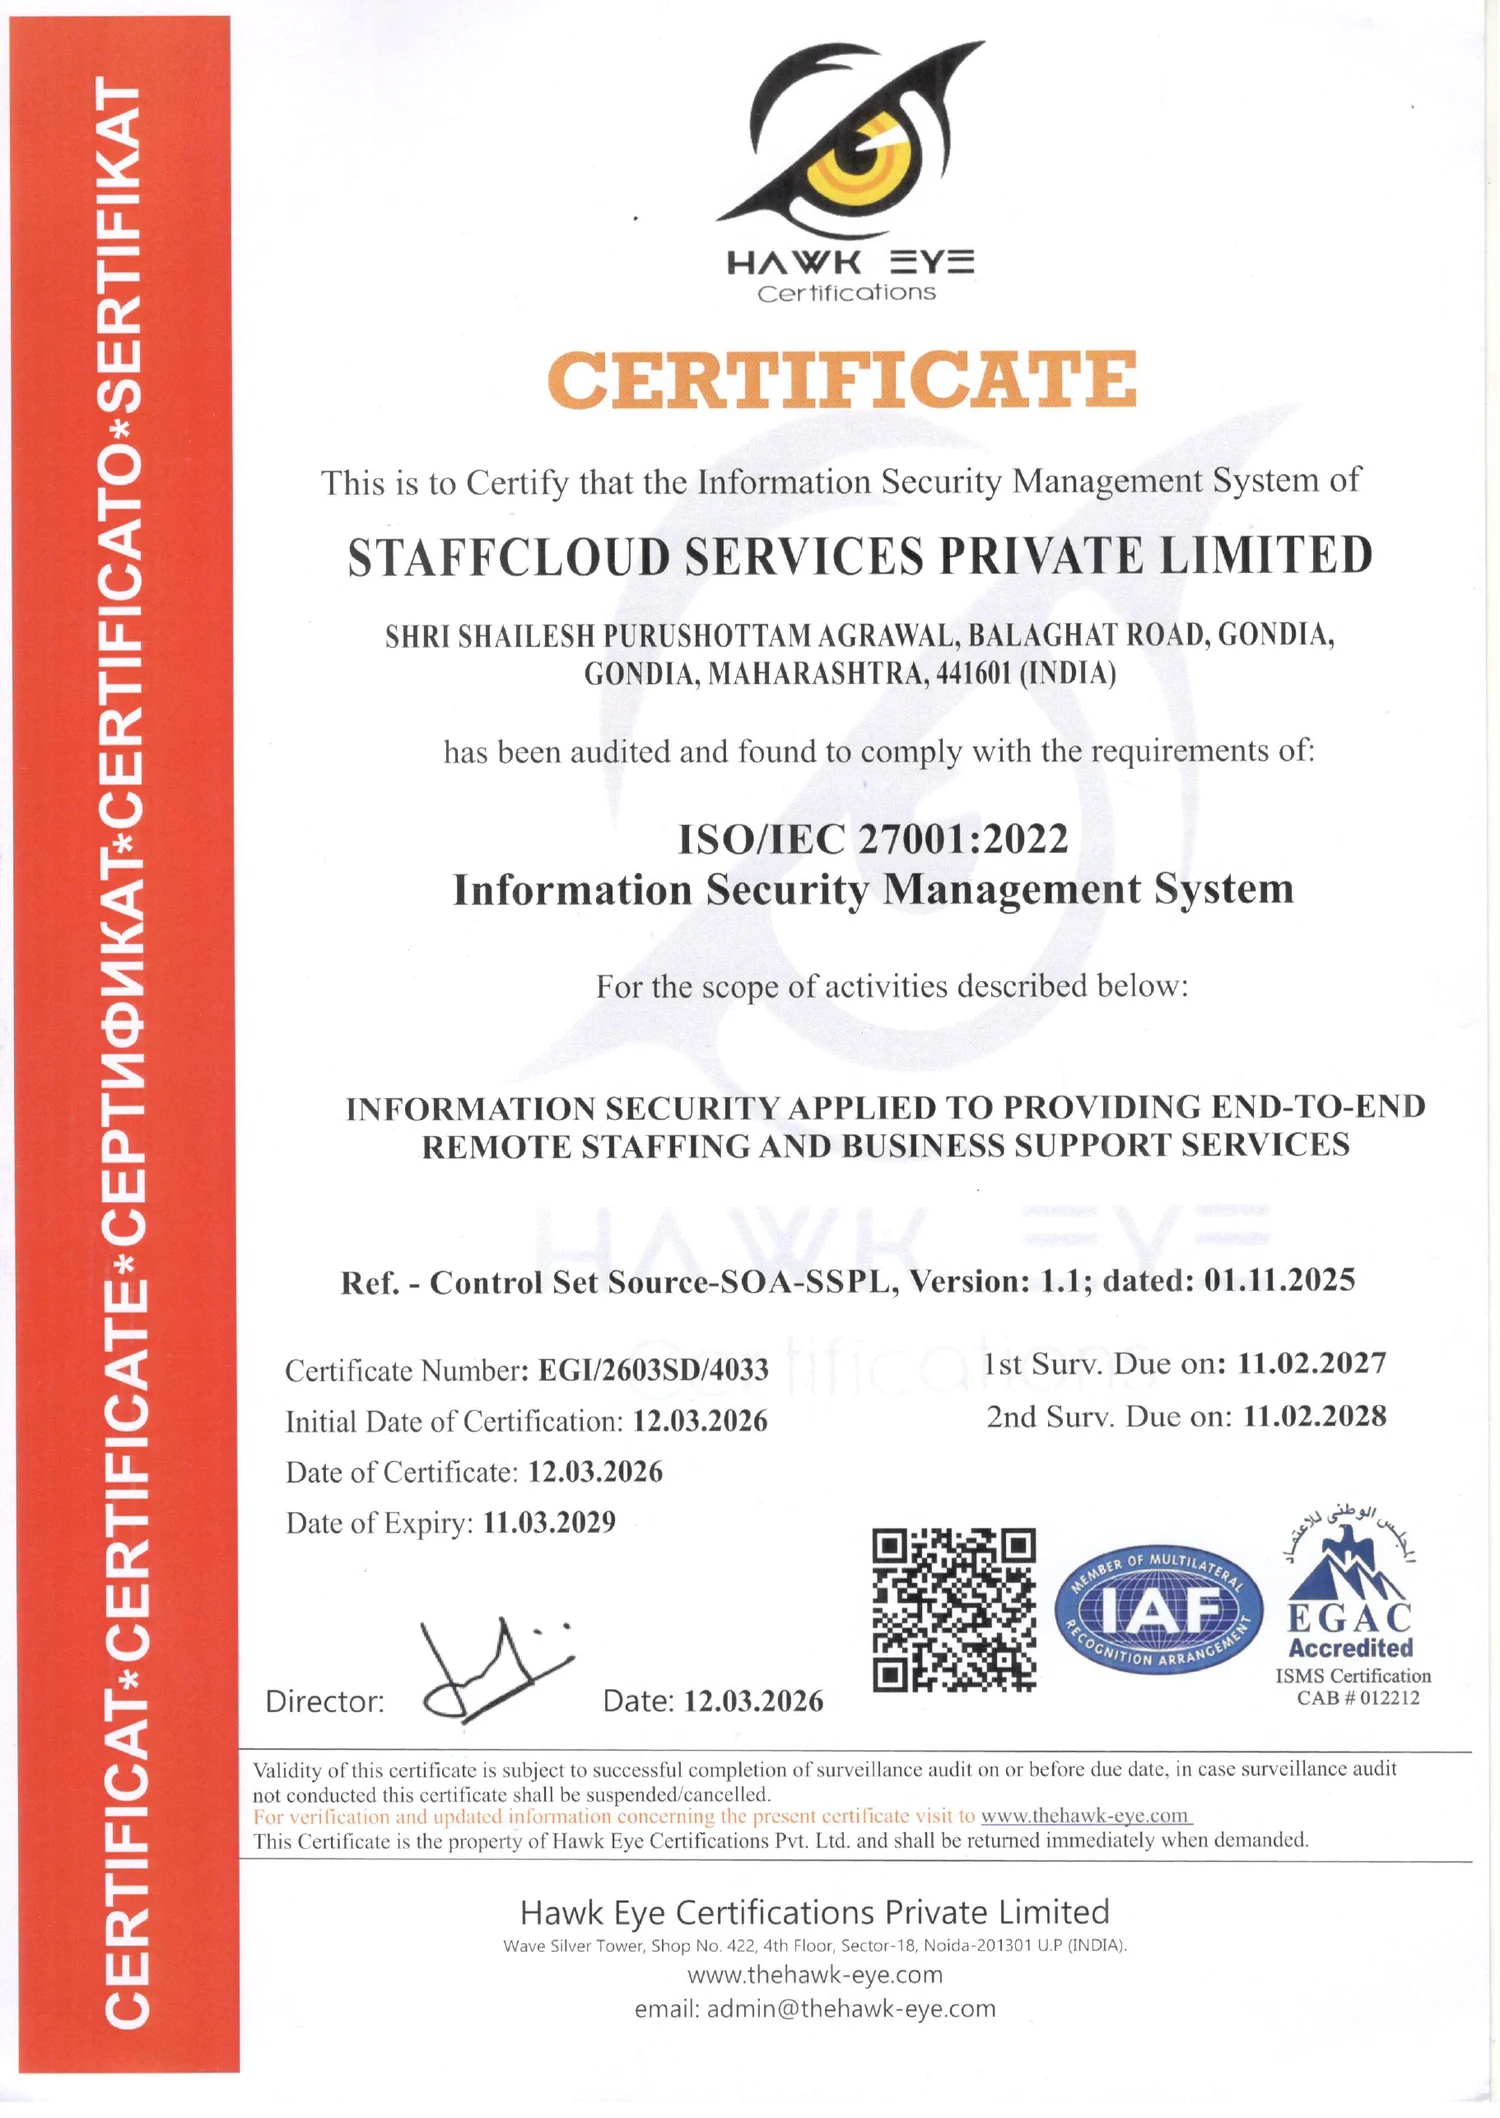
The ISO/IEC 27001:2022 certificate issued to StaffCloud Services Private Limited View certificate
Certificate number
EGI/2603SD/4033
Scope of certification
Information security applied to providing end-to-end remote staffing and business support services
Certification body
Hawk Eye Certifications Private Limited
Accreditation
EGAC accredited — ISMS certification, CAB #012212
Initial certification
12 March 2026
Valid until
11 March 2029
Surveillance audits due
11 February 2027 · 11 February 2028
Statement of Applicability
Control Set Source-SOA-SSPL, version 1.1, dated 1 November 2025
Download the PDF

ISO 9001:2015

Quality Management System

The quality counterpart: whether work comes out consistent, whether mistakes are caught before a client sees them, and whether a correction changes the process rather than just the output.

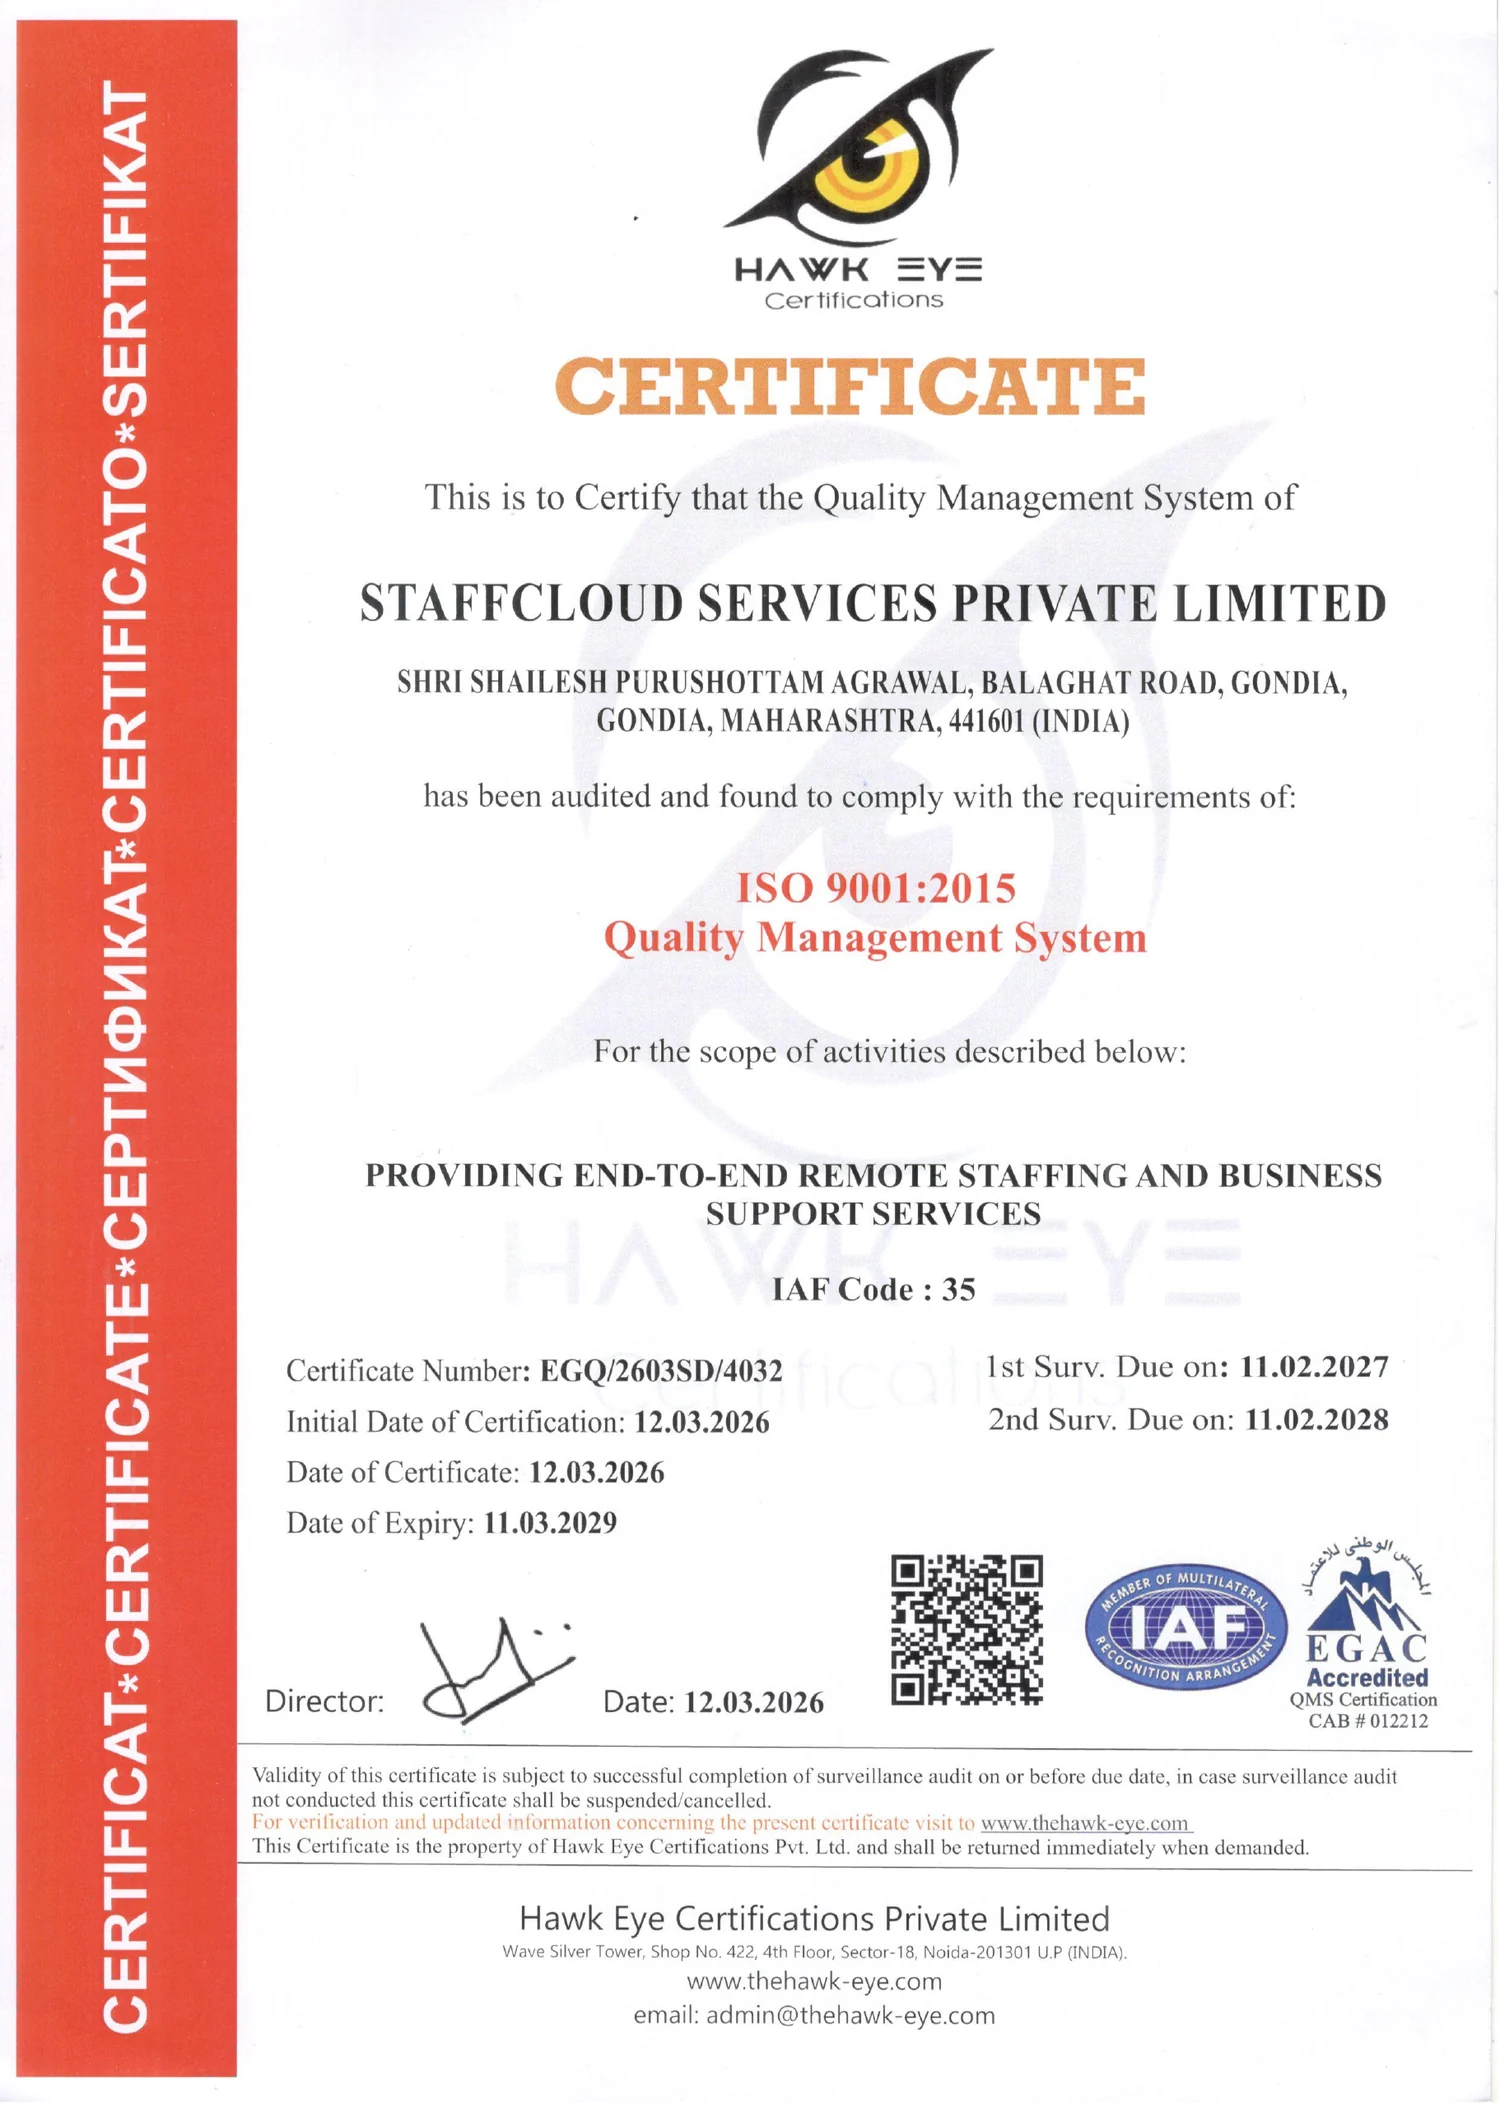
The ISO 9001:2015 certificate issued to StaffCloud Services Private Limited View certificate
Certificate number
EGQ/2603SD/4032
Scope of certification
Providing end-to-end remote staffing and business support services
Certification body
Hawk Eye Certifications Private Limited
Accreditation
EGAC accredited — QMS certification, CAB #012212
Initial certification
12 March 2026
Valid until
11 March 2029
Surveillance audits due
11 February 2027 · 11 February 2028
IAF code
35 — other services
Download the PDF

Both certificates are issued to StaffCloud Services Private Limited, Shri Shailesh Purushottam Agrawal, Balaghat Road, Gondia, Gondia, Maharashtra, 441601 (India).

Both certificates are valid subject to the surveillance audits above being completed on or before their due dates. A missed surveillance audit suspends or cancels the certificate — which is why the dates are published here rather than only the expiry.

Hawk Eye publishes current certificate status at thehawk-eye.com. The certificate number is what you look up, and both numbers are on this page.

What stands behind the certificates

Six commitments, each one citing the clause or the document it comes from — so you can check it rather than take it. Nothing on this page describes a control that is not written down somewhere you can read.

A managed ISMS, not a toolset

The certificate is against the management system: identified risks, chosen controls, named owners, and evidence of operation. The 2022 revision audits against a reorganised Annex A — organisational, people, physical and technological — including eleven controls that did not exist in the 2013 version.

ISO/IEC 27001:2022 certificate

Confidentiality that survives the engagement

Confidentiality obligations run for three years after an engagement ends, and indefinitely for source code, trade secrets and personal data. On termination or on written request, confidential material is returned or securely destroyed. Where you have your own NDA, it prevails over ours.

Terms, clause 17

Processor, under your instructions

Where we handle personal data, you are the controller and StaffCloud is the processor. We process it only to deliver the agreed services and only on your lawful written instructions — never for our own purposes, never sold. Access control, confidentiality undertakings from personnel and security awareness training are contractual, not aspirational.

Terms, clause 18.1–18.2

Breach notification without undue delay

On becoming aware of a personal-data breach affecting your data we notify you without undue delay, and co-operate in investigating, remediating and reporting it — including in responding to data principals, data-subject requests and regulators.

Terms, clause 18.4

Cross-border handling, named law

Delivery is from India for clients elsewhere, so personal data crosses a border and the engagement says so. The Digital Personal Data Protection Act, 2023 applies; where your engagement needs a data-processing addendum or standard contractual clauses, those terms are in the Service Agreement and prevail over our general terms.

Terms, clause 18.5

Re-performance as the remedy

Services are warranted to be performed with reasonable skill and care, and deliverables to conform materially to the specification for thirty days after delivery or acceptance. The remedy is that we re-perform or correct it — or refund that part where re-performing is not practicable. A named remedy is worth more than a quality promise.

Terms, clause 20.2

What a security review usually asks

Including the two questions most suppliers answer badly.

Hawk Eye Certifications Private Limited, of Noida, Uttar Pradesh, issued both. Hawk Eye is accredited by EGAC — the Egyptian Accreditation Council — under CAB number 012212, and EGAC is a signatory to the IAF Multilateral Recognition Arrangement, which is what the IAF mark on each certificate denotes.

Hawk Eye publishes current status at thehawk-eye.com; look up the certificate number. ISO/IEC 27001:2022 is EGI/2603SD/4033 and ISO 9001:2015 is EGQ/2603SD/4032. Both certificate PDFs are downloadable from this page, and each carries a QR code.

Surveillance audits are due 11 February 2027 and 11 February 2028, with the current certification cycle running to 11 March 2029. Validity is conditional on those audits happening on time — a missed surveillance audit suspends or cancels the certificate.

For ISO/IEC 27001:2022: information security applied to providing end-to-end remote staffing and business support services. For ISO 9001:2015: providing end-to-end remote staffing and business support services, IAF code 35. Both are scoped to the single Gondia site named on the certificates, which is the registered office — there is no second location to bring into scope.

No, and we would be wary of any supplier who told you it did. ISO/IEC 27001 certifies a managed information security system; GDPR is a legal obligation with its own requirements, and no certificate discharges it. What we can tell you is contractual: we act as processor on your instructions, the Digital Personal Data Protection Act, 2023 applies to us, and where your engagement needs a data-processing addendum or standard contractual clauses they go in the Service Agreement and override our general terms.

Under NDA, yes. The Statement of Applicability referenced on the ISO 27001 certificate is Control Set Source-SOA-SSPL version 1.1, dated 1 November 2025. Ask through the enquiry form and say what your security review needs.

No. The two ISO certificates on this page and the Clutch Premier Verified profile are the only credentials StaffCloud claims anywhere on this site. If a tender asks for something we do not hold, we will tell you that rather than describe ourselves as aligned with it.

Want to see the work rather than read about it?

Every client story on this site came out of a live account — a listing nobody could unblock, a chargeback nobody had time to dispute, a support queue that had outgrown the person holding it.

WhatsApp